eMudhra discloses compromise of 'weak' private keys behind eight certificates
Bengaluru certificate authority eMudhra disclosed that flawed key generation produced tiny, reverse-engineerable private keys behind eight intermediate certificates, now blocked by Apple, Google, Microsoft and Mozilla.
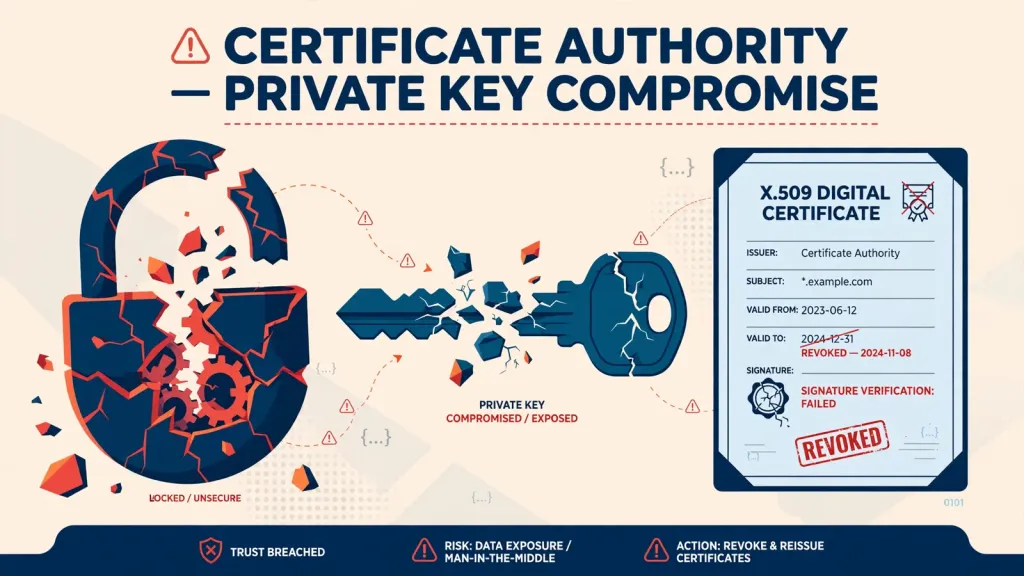
eMudhra, the Bengaluru-based tech company whose digital certificates browsers use to authenticate websites, has disclosed that “weak” private cryptographic keys linked to eight of its intermediate certificates were compromised, in a press release issued on October 21, 2026.
The private keys were created on April 30, 2025. eMudhra said a key-generation flaw produced a second set of weak keys alongside the original strong ones. Some of the weak keys were as small as the digit “four” - only 3 to 8 bits of strength, compared with the designed roughly 384 bits, equivalent to about 116 digits, of strength.
An independent researcher using the alias “Wayne” discovered that the weak keys could be reverse-engineered with AI-assisted techniques. He flagged the risk to Apple, Google, Microsoft and Mozilla, which have since blocked all eight intermediate certificates.
To demonstrate the compromise, Wayne created the domain emudhra.we-have-a-problem.com and on Tuesday posted a message signed using one of the compromised private keys. Browser makers, operating-system vendors, Cloudflare and others scrambled to issue updates in response.
Security experts warned that the compromised keys could be used to forge certificates for any domain and intercept supposedly secure connections, with some calling the compromise potentially catastrophic, according to the Indian Express (https://indianexpress.com/article/technology/tech-news-technology/cert-in-emudhra-certificate-compromise-catastrophic-say-experts-10930785/).
More on this topic: all Technology stories