ICO reprimands two Welsh bodies after 'Password1' test account exposed children's data
The ICO reprimanded Ogi Networks and Data Cymru after attackers used a test account called Test2 — password 'Password1', unchanged since 2012 — to breach data belonging to 3,300 people, mostly children.
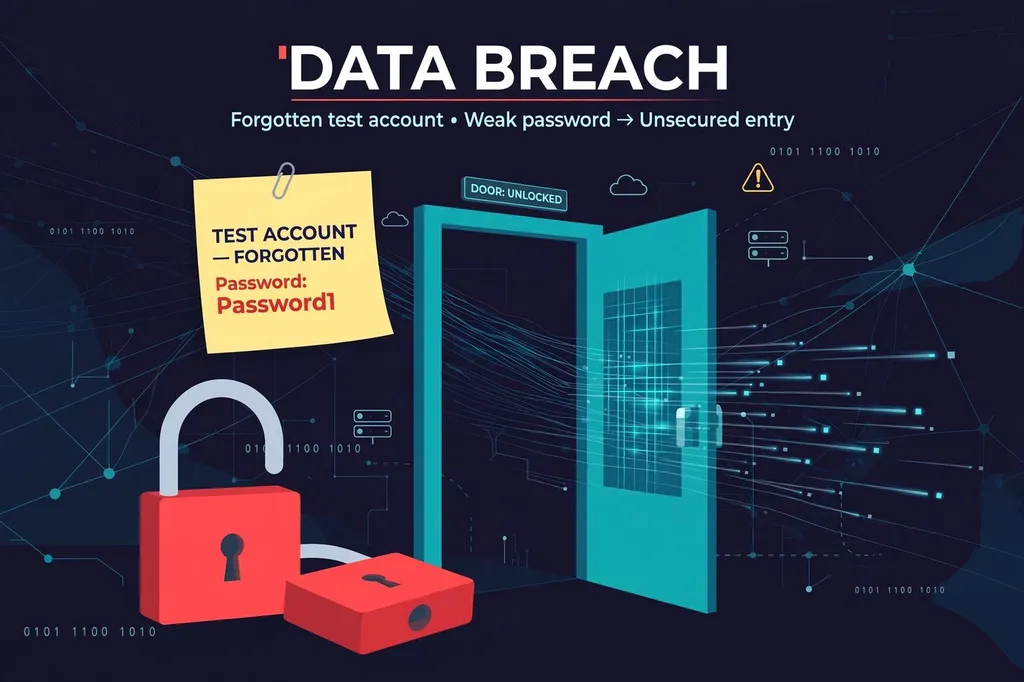
The UK Information Commissioner’s Office has reprimanded two Welsh organisations after attackers used a forgotten test account protected by the password “Password1” to steal personal data belonging to about 3,300 people, most of them children. The ICO issued reprimands rather than fines to Ogi Networks Limited (ONL) and the Local Government Data Unit – Wales, known as Data Cymru, in an announcement on Tuesday. (The Register; LocalGov)
The ransomware attack of 1 November 2024 exploited an account called Test2, created by ONL on 13 January 2012 during its initial Data Cymru project and never reviewed or removed in more than 12 years. The ICO cited Bitwarden’s password-strength tool, which rated “Password1” as “very weak” with a cracking time of under a second. (The Register)
Before deploying ransomware, the attackers exfiltrated 42 GB of data from a primary domain controller, a file server and an SQL server, and encrypted 182.7 GB. Local administrator accounts on three impacted systems all shared the same password, letting the intruder move laterally across the network. The compromised data related to two projects supporting children and families. (The Register; Infosecurity Magazine)
The ICO found ONL had failed to put in place appropriate technical and organisational measures under Article 32 of the UK GDPR, and that Data Cymru had no data-protection agreement with its IT supplier, leaving a responsibility gap. (The Register; Infosecurity Magazine)
“Password1 is not an appropriate password, it is a wide-open door to nefarious actors,” said David Doodson, the ICO’s head of investigations. “This incident shows how a single weak password, attached to an account that was no longer needed, can leave the door open to a serious cyber-attack that can affect thousands.” (The Register)
ONL said the test account “should have been removed long before criminals were able to use it”, and has since introduced multi-factor authentication and regular account reviews. Data Cymru, which merged with the Welsh Local Government Association in 2025, said there was no evidence the stolen information had been shared further or misused; it has since signed a compliant data-processing contract. (JournalArta; BritBrief)
More on this topic: all Technology stories